Quick answer: On Oct. 17, 2026, from about 22:04 UTC, attackers used NGRAVE’s own LIQUID app notifications to send fake ‘portfolio synced on a new device’ alerts that led to a seed-phrase phishing site, NGRAVE confirmed on X. Keys on the offline ZERO are safe unless users typed their recovery words. LIQUID is now under maintenance.
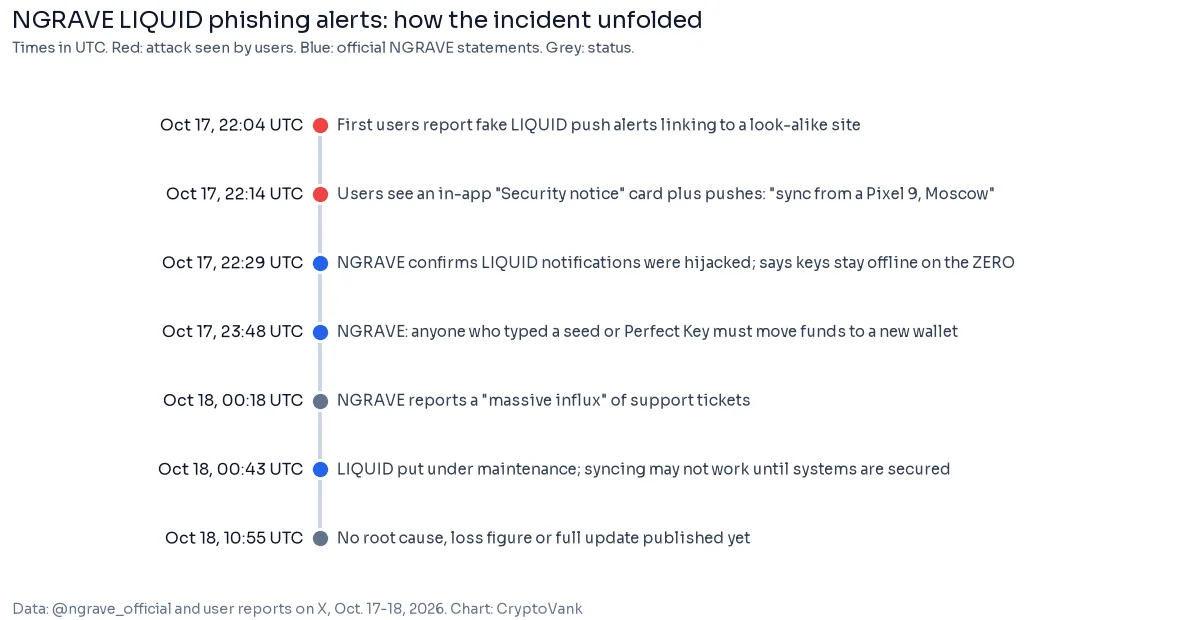
An NGRAVE phishing attack reached users through the company’s own app on Saturday night. From about 22:04 UTC on Oct. 17, 2026, owners of the NGRAVE ZERO hardware wallet began reporting push notifications from the official LIQUID companion app that sent them to a look-alike site asking for their recovery phrase.
At 22:29 UTC, NGRAVE confirmed on X that “LIQUID notifications [were] hijacked”. The alerts, it said, “are FAKE and built to steal your seed”. The Belgian wallet maker has not yet said how the attackers got in or whether anyone lost funds.
What did the NGRAVE phishing notifications say?
The lure was a security scare. For example, several users posted the same message: their “portfolio [was] synced on a new device”, a Pixel 9 in Moscow. One user, @passatordi, received three such pushes in a row.
In addition, another user, @IskanderXBT, said a “Security notice” card also appeared inside the app before the push arrived. The page showed the visitor’s real city and browser next to an invented attacker device, plus a 30-minute countdown. Both the Approve and Deny buttons led to the same form asking for a 24-word phrase or NGRAVE’s Perfect Key backup. We are not naming the scam domain, which still loaded at 10:55 UTC on Oct. 18.
Were NGRAVE wallets hacked?
So far, no evidence shows the ZERO device itself was breached. The ZERO is air-gapped and talks to LIQUID only through QR codes, while the app holds public addresses, not private keys, according to NGRAVE’s LIQUID page. NGRAVE told one worried user that “only the view wallet notification system” was compromised.
However, that is exactly what made the attack dangerous. A phishing link in an email can look fake, whereas this one arrived through the app users trust to manage a cold wallet. “The question is not the page but the channel,” @IskanderXBT wrote.
Did anyone lose money?
NGRAVE has not published a loss figure. At least one user replied to NGRAVE saying he had “lost everything”, but CryptoVank could not verify that claim. Later, at 00:18 UTC, the company reported a “massive influx” of support tickets.
What should you do after the NGRAVE phishing alert?
NGRAVE’s follow-up notice at 23:48 UTC splits users into two groups:
- You tapped the link but typed nothing: you are safe. The page only redirects, and the Deny button was part of the trick.
- You entered your seed or Perfect Key: treat it as compromised. Send your funds to a temporary wallet you control, reset your ZERO with a new Perfect Key, then move the funds back to the new addresses.
Meanwhile, NGRAVE also stressed that its only domain is ngrave.io and that it will never ask for recovery words. At 00:43 UTC on Oct. 18, it put LIQUID under maintenance “while we finish securing our systems”, so syncing may not work. A “full update” was promised but had not appeared by 10:55 UTC. For a refresher on safe habits, see our self-custody wallet setup guide.
What does this mean for hardware wallet users?
It is the third trust-channel attack on cold-wallet owners in days. Ledger is still dealing with tampered devices tied to $91 million in thefts, and Coldcard users were recently targeted by a fake migration notice from a hijacked X account. In each case, the hardware held firm and attackers went after the people around it.
As a result, the lesson is simple: no real wallet flow ever asks you to type recovery words into a phone or website. Our guide to spotting crypto scams and our checklist for confirming a hardware wallet is genuine cover the other warning signs.
NGRAVE Phishing FAQ
Is my NGRAVE ZERO safe after the LIQUID phishing alerts?
Yes, if you never typed your recovery words or Perfect Key anywhere. NGRAVE said on Oct. 17, 2026 that keys stay offline on the ZERO and that only LIQUID’s notification system was abused.
I tapped the fake NGRAVE notification. Am I at risk?
Not if you stopped there. NGRAVE says the page only redirects and cannot install anything; the danger was the form on the next page that asked for your 24 words or Perfect Key.
What should I do if I entered my seed phrase?
Assume it is compromised and act now. NGRAVE advises moving funds to a temporary wallet, resetting the ZERO with a new Perfect Key and sending the funds back to the new addresses.
Is the NGRAVE LIQUID app working now?
Not fully. NGRAVE put LIQUID under maintenance at 00:43 UTC on Oct. 18, 2026 and said syncing may not work until it finishes securing its systems.
Sources
- NGRAVE on X: security alert, LIQUID notifications hijacked (Oct. 17, 2026)
- NGRAVE on X: what to do if you tapped the link or entered your seed
- NGRAVE on X: LIQUID under maintenance (Oct. 18, 2026)
- NGRAVE on X: surge in support tickets
- NGRAVE: how LIQUID and ZERO work together
- @IskanderXBT on X: in-app card and phishing page details
- @passatordi on X: three fake push notifications
This article is for information only and is not financial or security advice. Details may change as NGRAVE investigates; DYOR and verify any warning through official channels.