Quick answer: A BTCPay Server hot wallet attack hit some self-hosted stores on Nov. 1, 2026. At 22:25 UTC, BTCPay told operators to shut down instances. Lead developer Nicolas Dorier said servers on 2.4.7 were not hit and reports involve versions older than 2.4.2, where attackers logged in as admin.
A BTCPay Server hot wallet warning went out late on Sunday, Nov. 1, 2026, and it was blunt: if you run an instance with a hot wallet, shut it down now. The free, self-hosted Bitcoin payment processor said attackers were sweeping funds from some merchant servers.
Early findings point to old, unpatched installs rather than the current release. However, the team still does not know how the attacker got in, so every operator should treat this as live.
What happened in the BTCPay Server hot wallet attack?
At 22:25 UTC on Nov. 1, the official BTCPay Server account on X posted that it was “receiving reports of hot wallets on BTCPay Servers being swept by unauthorized attackers.” It asked anyone running an instance to stop it with the ./btcpay-down.sh script until the investigation ends.
Minutes later, contributor Uncle Rockstar Developer repeated the alarm: “Not a drill: shut down your BTCPay Server if you have a hot wallet.” The Defiant and TokenPost also covered the alert.
A hot wallet in BTCPay keeps the wallet seed on the server itself, so the store can sign payouts and refunds without a hardware device. That is convenient, but anyone who controls the server can move the coins. Stores that only use a watch-only wallet, with keys kept offline, do not hold spendable keys on the box.
Which versions does the BTCPay Server hot wallet attack hit?
At 00:28 UTC on Nov. 2, lead developer Nicolas Dorier gave the first details: “Our public servers were not attacked (on 2.4.7), it seems reports are on before 2.4.2. The attacker managed to log in as admin on those instance, we are still trying to figure out how.”
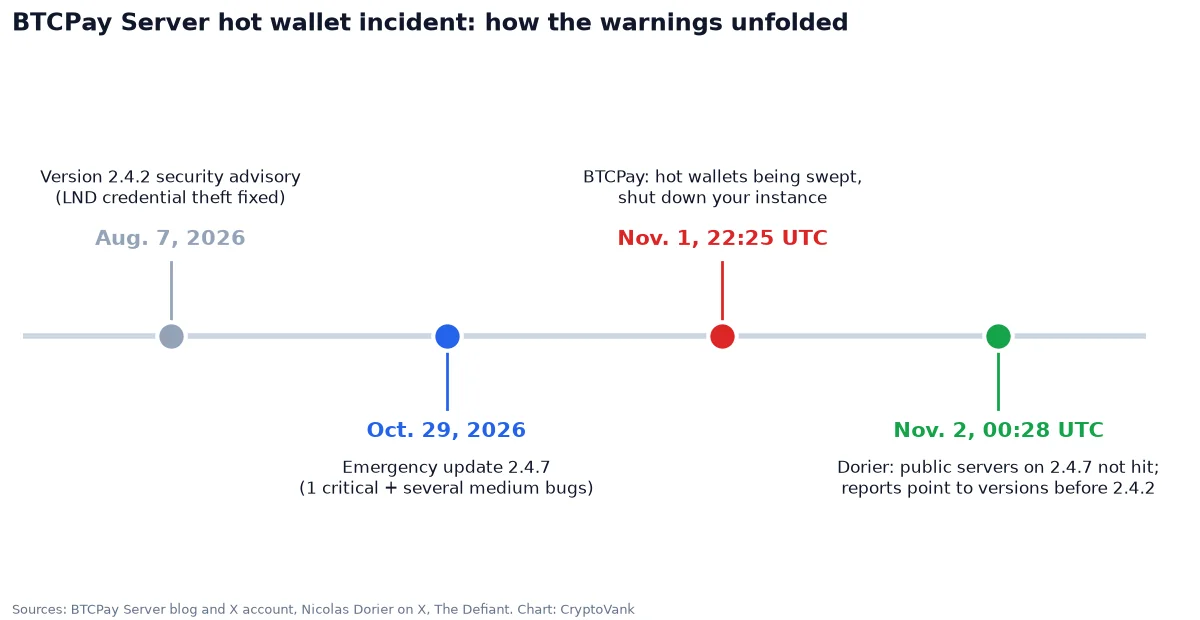
That lines up with recent patches. On Aug. 7, 2026, the team published a security advisory for 2.4.2, which fixed a flaw that let attackers steal Lightning (LND) credentials. Then, on Oct. 29, BTCPay shipped emergency release 2.4.7, which fixed one critical and several medium bugs found with an AI code scanner.
In short, servers that skipped months of updates look most exposed. Still, the exact entry point is unknown, and the team has not shared a loss total or a count of affected stores.
What should merchants do about a BTCPay Server hot wallet?
Here is a short checklist based on the team’s guidance and basic hot wallet hygiene:
- Shut down first. Run
./btcpay-down.shif your store holds a hot wallet, as the team asked. - Check your version. Anything older than 2.4.2 matches the reports. Plan to move to the latest release once the team gives the all-clear.
- Review admin accounts. Look for unknown admin users or logins, and change passwords and API keys.
- Move funds after the fix. Once the cause is known, sweep remaining coins to a wallet whose keys never touch the server.
- Watch official channels. Dorier said the team “will communicate more on btcpayserver account soon.”
For the basics of keeping keys offline, see our guide on what a seed phrase is and how to store it. Self-hosted Bitcoin tools have been a target lately; we recently covered the Electrum 4.8.3 malicious server bug and how Bitcoin Core is handling AI-found bugs.
Does the BTCPay Server attack affect the Bitcoin price?
No, not so far. At 00:54 UTC on Nov. 2, CoinGecko showed Bitcoin at $78,060, up 0.64% in 24 hours. This is a software incident at individual merchants, not a flaw in the Bitcoin network.
Even so, the market implications are real for Bitcoin payments. BTCPay is one of the most common ways for shops to accept BTC without a middleman. If losses grow, some merchants may switch to custodial processors or turn off hot wallets for good. Meanwhile, the incident adds to a heavy year for crypto theft, as our report on $1.18 billion in Q3 hacks showed.
BTCPay Server Hot Wallet FAQ
Is BTCPay Server hacked?
Attackers broke into some self-hosted instances. BTCPay said on Nov. 1, 2026 that attackers were sweeping hot wallets on certain servers. According to Nicolas Dorier, attackers did not hit its own public servers on version 2.4.7.
Which BTCPay versions are affected?
Early reports involve versions older than 2.4.2, according to Dorier. The team is still investigating how attackers logged in as admin, so it asked all operators to shut down hot wallet instances.
Are watch-only BTCPay wallets safe?
A watch-only wallet keeps no spendable keys on the server, so the reported sweeps targeted hot wallets. The team has not yet ruled on other risks, so follow its next update.
How do I shut down BTCPay Server?
The team asked operators to run the ./btcpay-down.sh script on their server. Keep it offline until BTCPay publishes the cause and a fix.
Sources
- BTCPay Server on X: hot wallet sweep alert (Nov. 1, 2026)
- Nicolas Dorier on X: update on affected versions (Nov. 2, 2026)
- Uncle Rockstar Developer on X: shutdown warning
- The Defiant: BTCPay Server urges shutdown after hot wallet sweeps
- TokenPost: BTCPay Server hot wallet alert
- BTCPay Server blog: Security advisory for 2.4.2
- CoinGecko: Bitcoin price data
Not financial advice. Crypto is volatile; always do your own research (DYOR) before trading.